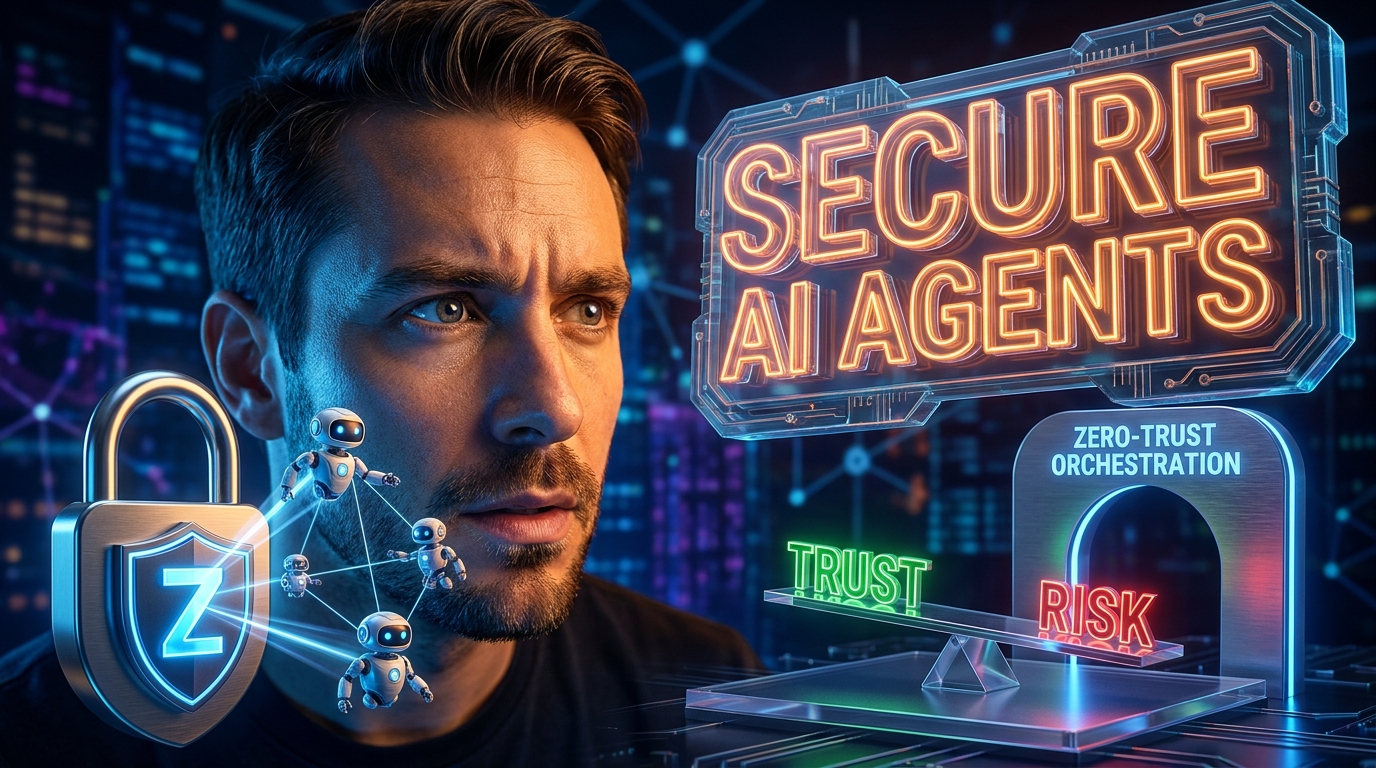

The global financial services ecosystem stands on the threshold of an unprecedented architectural paradigm shift. Autonomous artificial intelligence (AI) agents are rapidly evolving from isolated decision-support utilities into autonomous transacting entities. These agents analyze real-time market microstructure, automate cross-border settlement routes, originate algorithmic credit facilities, and execute high-frequency arbitrage across disparate liquidity pools. However, delegating high-stakes transactional execution to autonomous agents exposes significant vulnerabilities in traditional cybersecurity and compliance architectures.
Perimeter-based network defenses are structurally inadequate for distributed, multi-agent systems operating across hybrid clouds, proprietary legacy mainframes, and decentralized ledgers. When autonomous agents operate with ambient authority or static credentials, a single compromised model weights vector, adversarial prompt injection, or data poisoning exploit can propagate catastrophic systemic failure across interlinked financial institutions. Establishing secure, compliant, and resilient financial automation demands a transformative approach: the Zero-Trust Interoperability Framework.
The Critical Imperative: Zero-Trust for Agentic Financial Networks
Traditional cybersecurity architectures rely on perimeter-based security models where interior network actors inherit broad implicit trust. In an autonomous financial deployment, this implicit trust creates catastrophic systemic risk. Autonomous AI agents operate without biological intuition; they process instructions at machine speed and cannot discern social context or high-level fiduciary duties unless strictly bounded by deterministic cryptographic constraints.
Implementing the Zero-Trust security paradigm—governed by the core tenant of never trust, always verify—redefines how machine-to-machine interactions occur in capital markets and retail banking. Under this model, every incoming data vector, outgoing settlement instruction, inter-agent inference request, and API call must be continuously authenticated, strictly authorized, and cryptographically verified prior to execution.
- Cryptographic Workload Identity: AI agents are provisioned with short-lived, verifiable identity credentials (utilizing standards such as SPIFFE/SPIRE) rather than persistent API keys or broad database access tokens.
- Continuous Contextual Verification: Agent interactions are evaluated in real time against dynamic risk telemetry, including model behavioral drift, geographic origin, payload anomaly scoring, and market volatility indices.
- Dynamic Least-Privilege Enforcement: Agents execute transactions under micro-scoped authorization boundaries that automatically scale down permissions during periods of heightened systemic or model uncertainty.
- Strict Network Micro-Segmentation: Transacting environments are isolated into cryptographic enclaves, ensuring that an adversarial breach within an analytics agent cannot compromise treasury execution services.
Architecting Cross-System Interoperability for Heterogeneous Finance
Autonomous agents must rarely operate in isolation. A standard automated trade lifecycle involves orchestrating data across multiple fragmented environments: parsing real-time market feeds, consulting private risk models, validating KYC/AML databases, querying SWIFT or ISO 20022 clearing gateways, and updating core accounting ledgers. Interoperability without rigorous governance creates unmanageable attack vectors.
The Zero-Trust Interoperability Framework bridges disparate infrastructure layers by implementing secure proxy mediation and canonical translation protocols. Rather than exposing native database connectors or broad API endpoints, financial institutions deploy hardened sidecar architectures and secure mediation gateways. These proxies normalize disparate data formats (e.g., FIX, FpML, JSON-RPC, ISO 20022) into cryptographically signed transaction envelopes before ingestion by autonomous agents.
The Zero-Trust Interoperability Architectural Comparison
To understand the structural advantages of a Zero-Trust Interoperability Framework, institutions must evaluate how it fundamentally differs from legacy architectural models across key operational parameters:
Test Agent Primitive
See the concepts from this article in action. No login required.
| Capability Dimension | Perimeter-Based Architecture | Standard API Gateway Architecture | Zero-Trust Interoperability Framework |
|---|---|---|---|
| Identity Verification | Static credentials, IP whitelisting, perimeter firewalls | Bearer tokens (OAuth2/JWT) with broad multi-resource scope | Short-lived, mutual-TLS (mTLS) cryptographic identities per agent interaction |
| Authorization Model | Implicit internal trust; full lateral movement upon breach | Role-Based Access Control (RBAC) with broad static access grants | Attribute-Based Access Control (ABAC) and Open Policy Agent (OPA) dynamic runtime rules |
| Payload Inspection | Edge inspection only; unmonitored lateral internal traffic | Syntactic JSON/XML schema validation at perimeter | Deep semantic payload analysis, adversarial prompt filtration, and deterministic boundary checks |
| Blast Radius Mitigation | Severe; full lateral network compromise possible | Moderate; bounded to API scope permissions | Zero lateral mobility; dynamic micro-segmentation and ephemeral compute sandboxing |
| Auditability & Provenance | Fragmented, non-standardized application logs | Centralized gateway access logs | Cryptographically chained, tamper-evident distributed ledgers with complete inference context |
Enforcing Deterministic Guardrails on Nondeterministic AI
Large Language Models (LLMs) and advanced neural network architectures are inherently probabilistic. In contrast, financial execution systems and regulatory frameworks demand absolute determinism, mathematical predictability, and strict adherence to rulebooks. This structural dichotomy represents the core friction point in deploying agentic AI across capital markets.
The Zero-Trust Interoperability Framework addresses this friction by inserting deterministic policy-as-code guardrails directly into the inter-system communication loop. Before an autonomous agent can emit a signed instruction to an execution broker or payments gateway, the transaction payload must pass through independent, rule-based verification engines (e.g., Open Policy Agent engines running WebAssembly filters). These engines enforce absolute structural limits:
- Notional Value Caps: Strict, unalterable hard limits on single-transaction and cumulative daily volume execution per agent.
- Slippage and Spread Boundaries: Real-time mathematical checks that abort execution if market conditions deviate from predefined risk models.
- Sanctions and Compliance Screening: Automated, real-time validation against global sanctions lists, PEP databases, and cross-border capital flow restrictions.
- Model Confidence Validation: Automated rejection of execution payloads if the originating model's epistemic confidence score falls below strict statistical thresholds.
Regulatory Harmonization: AI Act, DORA, and Immutable Auditability
As global financial regulators pivot toward proactive algorithmic oversight, institutions deploying autonomous agents face intensive reporting and risk management mandates. The European Union's Artificial Intelligence Act classifies AI models used for credit scoring, risk pricing, and life insurance underwriting as high-risk systems, mandating continuous data governance, detailed technical logging, and human-in-the-loop oversight mechanisms.
Simultaneously, the Digital Operational Resilience Act (DORA) requires financial entities to maintain complete operational control, business continuity, and comprehensive third-party ICT risk management. An ad-hoc autonomous agent architecture cannot survive regulatory scrutiny under these frameworks.
The Zero-Trust Interoperability Framework guarantees compliance by establishing continuous, immutable provenance logging. For every transaction executed by an autonomous agent, the framework generates a cryptographic audit record containing:
- The exact model version, weights hash, and training metadata provenance.
- The snapshot of contextual prompt inputs, external API telemetry, and intermediate reasoning steps.
- The mTLS cryptographic identity of the sending agent and the receiving service.
- The deterministic policy evaluation output proving compliance at the exact millisecond of execution.
Strategic Implementation Blueprint for Financial Enterprises
Deploying a Zero-Trust Interoperability Framework requires a systematic, phased engineering methodology. Financial institutions should avoid disruptive rip-and-replace deployments in favor of progressive architectural modernization:
Phase 1: Identity and Policy Baseline. Decouple static credentials from all existing automated scripts and microservices. Establish a unified identity control plane using SPIFFE/SPIRE to issue short-lived cryptographic identities to workloads, microservices, and autonomous agents across on-premises and multi-cloud footprints.
Phase 2: Micro-Segmentation and Sidecar Interception. Introduce sidecar service proxies to mediate all inter-service and cross-agent communications. Enforce mutual TLS (mTLS) with strict cipher suites, ensuring that all data in transit across legacy core systems and modern AI workloads is authenticated and encrypted end-to-end.
Phase 3: Deterministic Policy Integration. Implement dynamic policy engines that intercept transactions downstream of AI agent inference engines. Define enterprise-wide risk limits, regulatory compliance checks, and structural guardrails via declarative, version-controlled policy-as-code repositories.
Phase 4: Tamper-Evident Telemetry and Continuous Assurance. Integrate cryptographic telemetry pipelines that stream inference metadata, authorization traces, and execution receipts into immutable, WORM-compliant (Write Once, Read Many) log archives. Conduct continuous red-teaming, adversarial prompt injection tests, and automated disaster recovery simulations to ensure systemic operational resilience.
By unifying Zero-Trust security principles with robust interoperability protocols, financial institutions can safely harness the transformative efficiency of autonomous AI. This architectural foundation ensures that as algorithmic systems increasingly manage the velocity of global capital, they do so within an unbreachable framework of cryptographic trust, deterministic safety, and uncompromising regulatory compliance.
Ready to Build?
Stop guessing. Start building. Every new account gets 1,000 NOVA credits instantly upon login to test the registry and route intents.
Claim 1,000 Credits →