
The Autonomous Finance Imperative and the Accountability Deficit
The contemporary financial landscape is defined by the transition from human-supervised automation to fully autonomous agentic workflows. In quantitative trading, institutional lending, anti-money laundering (AML) surveillance, and dynamic liquidity management, machine learning models and multi-agent systems are increasingly entrusted with mission-critical capital decisions. However, granting operational autonomy to non-deterministic, high-capacity models introduces unprecedented systemic vulnerabilities.
When an autonomous agent executes high-volume market transactions or denies credit facility access within milliseconds, conventional post-hoc audit frameworks collapse. Deep neural networks, reinforcement learning policies, and large language models (LLMs) operate as sophisticated 'black boxes.' In the absence of strict execution guardrails and rigorous architectural isolation, enterprise AI teams face severe exposures: algorithmic collusion, hallucinations, cascading flash-crash scenarios, and catastrophic regulatory non-compliance.
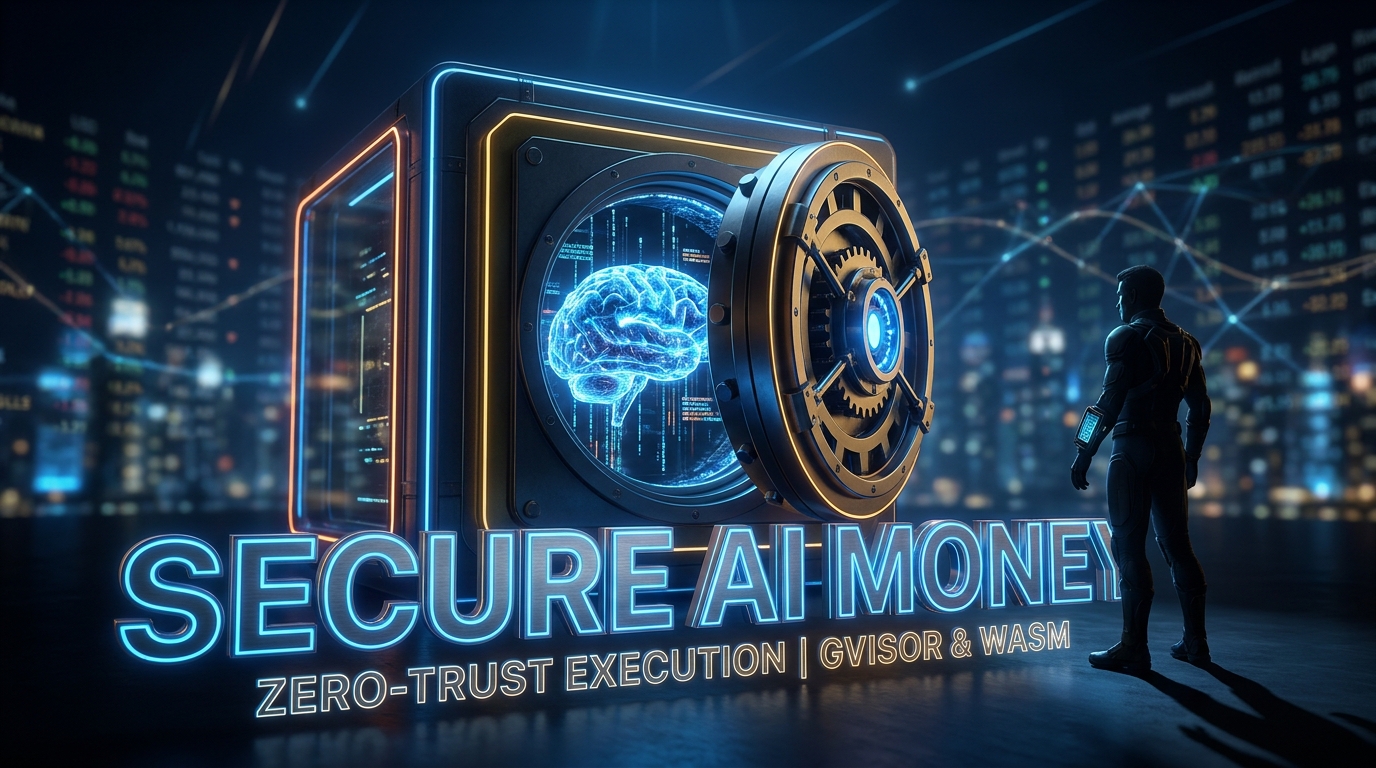
To deploy autonomous finance at enterprise scale, institutions must resolve the fundamental tension between computational agency and risk containment. This requires moving beyond perimeter-based defensive models and adopting a purpose-built architectural paradigm: the Zero-Trust AI Sandbox.
Anatomizing the Zero-Trust AI Sandbox Architecture
A Zero-Trust AI Sandbox is not merely an isolated test harness; it is a continuously governed execution fabric designed to run cognitive workloads under absolute programmatic verification. Rooted in the foundational Zero-Trust principle—'never trust, always verify'—this architecture strips autonomous agents of any implicit network, data, or operational access privileges.
Core Architectural Pillars
- Least-Privilege Contextual Access: Autonomous agents are provisioned with ephemeral, micro-scoped credentials. An agent tasked with assessing counterparty credit risk is cryptographically prohibited from accessing algorithmic trade execution rails or unmasked customer identifiable data (PII).
- Deterministic Runtime Isolation: Agents execute within hardened, containerized micro-virtual machines (microVMs) or secure enclaves. These environments dynamically restrict compute, system calls, and egress pathways, ensuring that anomalous behavior cannot breach external infrastructure.
- Continuous Identity and Behavioral Attestation: The sandbox continuously monitors the integrity of the underlying model weights, runtime configurations, and real-time inference patterns. Any sudden divergence in output entropy or unexpected tool-calling triggers automated execution throttling.
- Immutable Cryptographic Audit Trails: Every internal state transition, input tensor, model inference, and tool invocation is recorded on an append-only, tamper-evident telemetry ledger, establishing undeniable operational lineage.
Mechanizing Explainability: Deep Explainable AI (XAI) Integration
Accountability in autonomous financial systems is inextricably linked to interpretability. A decision that cannot be mathematically or logically justified to an internal risk committee or a sovereign financial regulator is an unacceptable operational liability. Zero-Trust Sandboxes bridge this divide by baking explainability engines directly into the runtime pipeline.
Test Agent Primitive
See the concepts from this article in action. No login required.
Mathematical Interpretability at Runtime
Rather than treating explainability as an external post-processing step, the sandbox captures feature attributions in real time. Techniques such as Shapley Additive Explanations (SHAP), Integrated Gradients, and deterministic counterfactual analysis are integrated directly into the inference validation pipeline:
- Local Feature Attribution: Deconstructs individual inference events to establish precisely how specific macroeconomic indicators, volatility metrics, or credit histories influenced an agent's discrete output.
- Global Model Transparency: Surfaces latent shifts in feature importance distributions across rolling production batches, alerting quantitative risk teams to underlying concept drift and training-data decay.
- Counterfactual Generation: Automatically calculates the minimum perturbation required in input data to alter the autonomous decision, providing actionable insight for compliance reporting and dispute remediation.
Structural Comparison: Traditional Sandboxes vs. Zero-Trust AI Sandboxes
| Operational Dimension | Traditional Software Sandbox | Zero-Trust AI Sandbox |
|---|---|---|
| Trust Verification | Implicit trust granted once inside the environment perimeter. | Zero implicit trust; continuous authentication for every model query and tool call. |
| Isolation Mechanism | Static network VLANs and shared virtual infrastructure. | Hardware-enforced enclaves, ephemeral microVMs, and system-call filtering. |
| Observability Depth | Basic operating system logs and API request/response metrics. | Tensor-level telemetry, internal weight attestation, and continuous latency-aware XAI. |
| Data Governance | Static snapshots or manual anonymized data dumps. | Dynamic data synthesis, on-the-fly tokenization, and strict egress diodes. |
| Safety Automation | Manual kill-switches and static operational thresholds. | Automated circuit breakers, divergence detectors, and runtime behavioral sandboxing. |
Enterprise Implementation Blueprint: From Evaluation to Production
Transitioning autonomous financial agents from initial design to live execution rails demands a staged, governance-driven deployment model. Financial engineering teams must systematically eliminate operational friction while validating safety parameters.
Phase 1: Synthetic Stress-Testing and Boundary Probing
Models are deployed within isolated sandboxes populated entirely by generative adversarial market simulators. Agents are subjected to extreme tail-risk conditions, simulated liquidity freezes, and adversarial data-injection attacks to map out their behavioral failure modes and boundary constraints.
Phase 2: Dark-Launch and Shadow Routing
The autonomous agent processes live market feeds and operational data streams in parallel with existing legacy systems or human operators. The sandbox operates in a zero-execution mode: inferences, feature attributions, and intended actions are captured and analyzed in real time without allowing external execution against institutional balance sheets.
Phase 3: Gated Execution with Autonomous Circuit Breakers
The agent is granted restricted production clearance under real-time policy governors. Dynamic circuit breakers continuously monitor trade sizes, slippage metrics, portfolio risk thresholds, and explainability consistency scores. If the agent's decision confidence drops below predetermined thresholds or if feature distributions deviate unexpectedly, execution is halted instantly and routed for human-in-the-loop (HITL) authorization.
Regulatory Alignment and Future-Proofing Capital Markets
Global regulatory frameworks are aggressively tightening around artificial intelligence in financial services. Frameworks such as the European Union AI Act, the SEC's proposed algorithmic conflict-of-interest rules, and the Basel Committee on Banking Supervision (BCBS) standards demand unassailable operational resilience, comprehensive traceability, and demonstrable human oversight.
Deploying autonomous finance systems inside a Zero-Trust AI Sandbox directly fulfills these statutory requirements. By transforming opaque neural networks into continuously attested, fully auditable, and mathematically interpretable systems, financial institutions can aggressively capitalize on autonomous capabilities while systematically insulating their capital, reputation, and stakeholders from systemic algorithmic risk.
Ready to Build?
Stop guessing. Start building. Every new account gets 1,000 NOVA credits instantly upon login to test the registry and route intents.
Claim 1,000 Credits →